← Notebook On this page 1. Identity Aware Network Security Framework# Asset & Trust Context
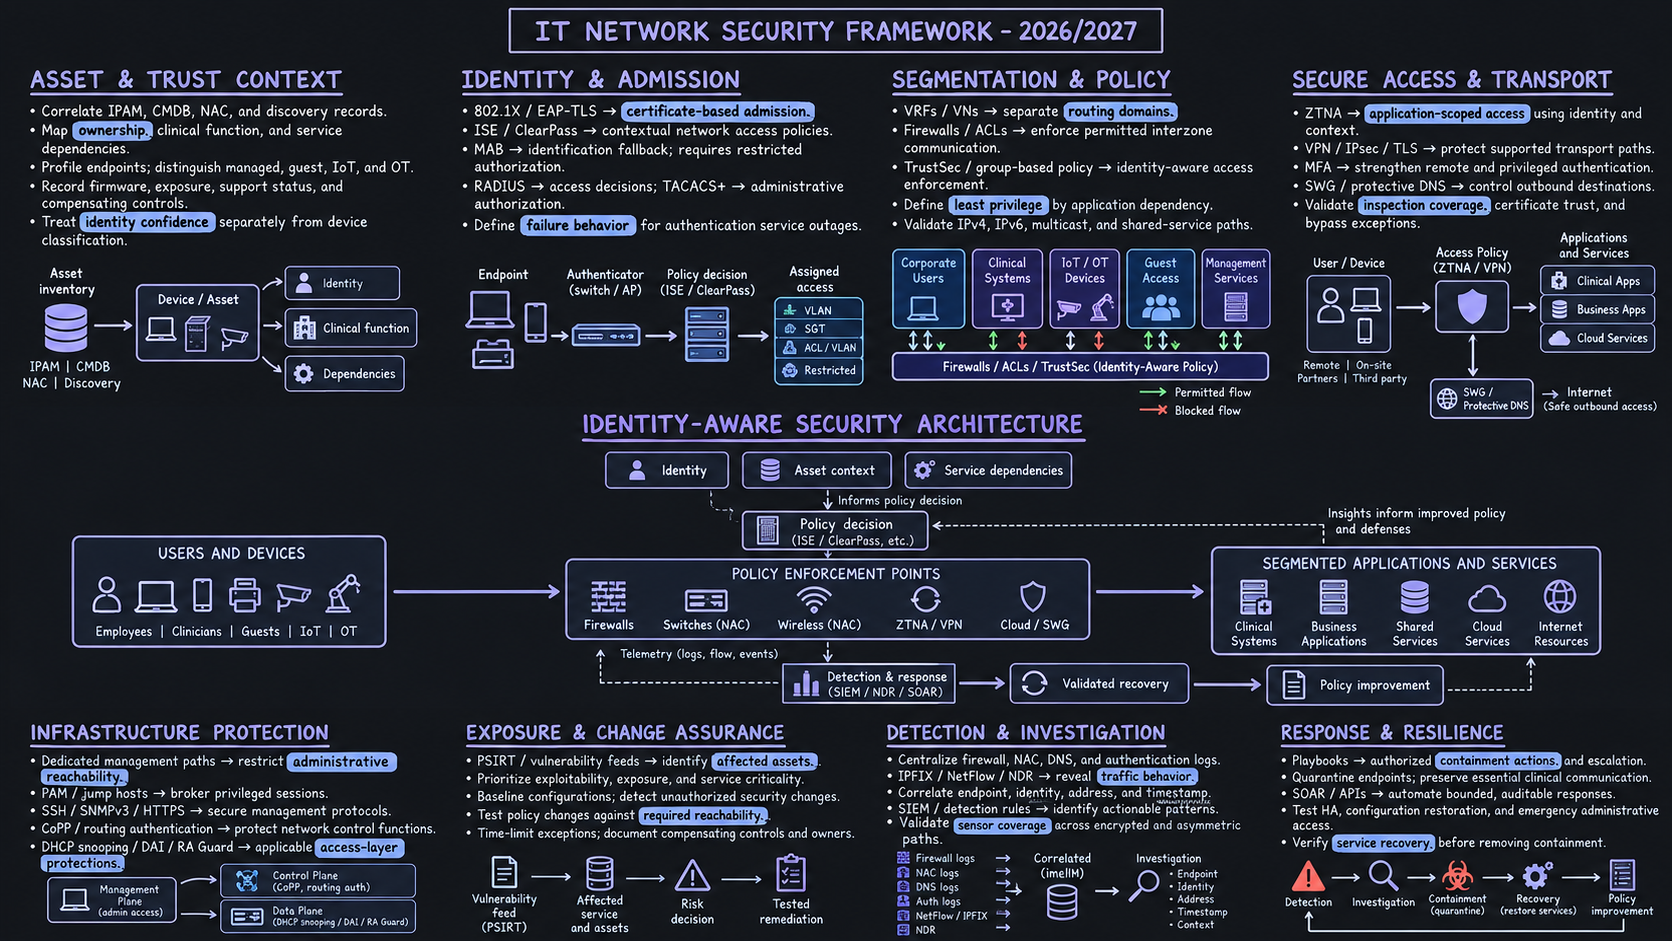
Correlate IPAM, CMDB, NAC, and discovery records. Map ==ownership==, clinical function, and service dependencies. Profile endpoints; distinguish managed, guest, IoT, and OT. Record firmware, exposure, support status, and compensating controls. Treat ==identity confidence== separately from device classification. Identity & Admission
802.1X / EAP-TLS → ==certificate-based admission==. ISE / ClearPass → contextual network access policies. MAB → identification fallback; requires restricted authorization. RADIUS → access decisions; TACACS+ → administrative authorization. Define ==failure behavior== for authentication service outages. Segmentation & Policy
VRFs / VNs → separate ==routing domains==. Firewalls / ACLs → enforce permitted interzone communication. TrustSec / group-based policy → identity-aware access enforcement. Define ==least privilege== by application dependency. Validate IPv4, IPv6, multicast, and shared-service paths. Secure Access & Transport
ZTNA → ==application-scoped access== using identity and context. VPN / IPsec / TLS → protect supported transport paths. MFA → strengthen remote and privileged authentication. SWG / protective DNS → control outbound destinations. Validate ==inspection coverage==, certificate trust, and bypass exceptions. Infrastructure Protection
Dedicated management paths → restrict ==administrative reachability==. PAM / jump hosts → broker privileged sessions. SSH / SNMPv3 / HTTPS → secure management protocols. CoPP / routing authentication → protect network control functions. DHCP snooping / DAI / RA Guard → applicable ==access-layer protections==. Exposure & Change Assurance
PSIRT / vulnerability feeds → identify ==affected assets==. Prioritize exploitability, exposure, and service criticality. Baseline configurations; detect unauthorized security changes. Test policy changes against ==required reachability==. Time-limit exceptions; document compensating controls and owners. Detection & Investigation
Centralize firewall, NAC, DNS, and authentication logs. IPFIX / NetFlow / NDR → reveal ==traffic behavior==. Correlate endpoint, identity, address, and timestamp. SIEM / detection rules → identify actionable patterns. Validate ==sensor coverage== across encrypted and asymmetric paths. Response & Resilience
Playbooks → authorized ==containment actions== and escalation. Quarantine endpoints; preserve essential clinical communication. SOAR / APIs → automate bounded, auditable responses. Test HA, configuration restoration, and emergency administrative access. Verify ==service recovery== before removing containment. Central Visual
Identity-aware security architecture : Users and devices request access through policy enforcement points to segmented applications and services. Identity, asset context, and service dependencies inform decisions. Telemetry feeds detection and response; validated recovery feeds policy improvement.