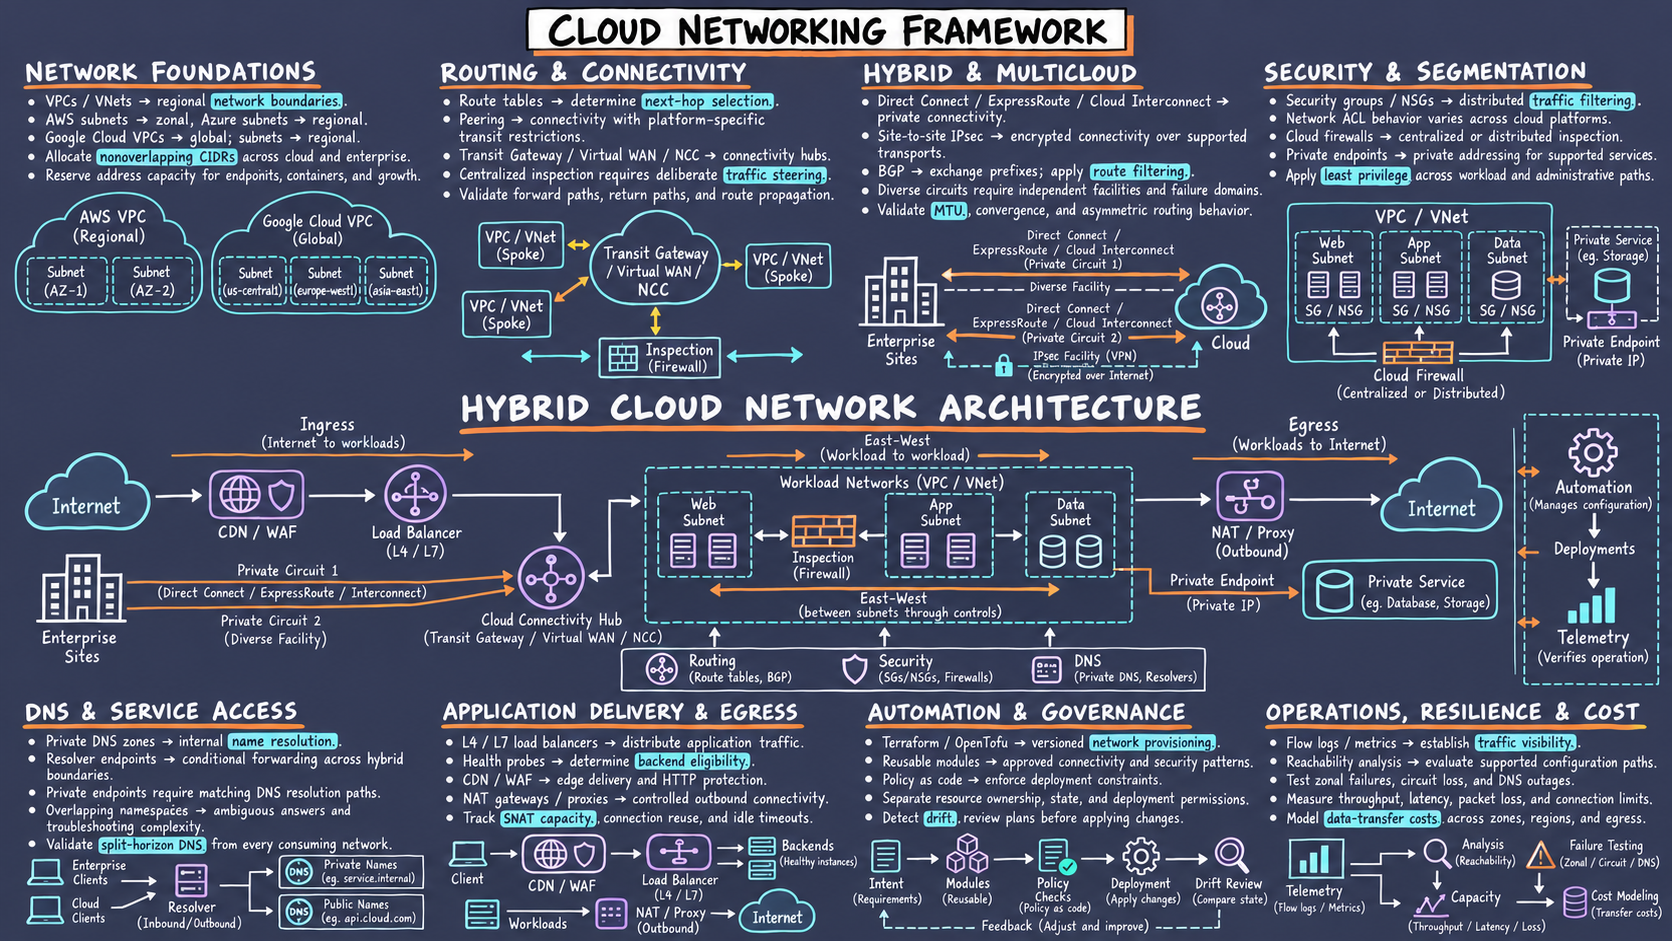
Network Foundations
- VPCs / VNets → regional ==network boundaries==.
- AWS subnets → zonal; Azure subnets → regional.
- Google Cloud VPCs → global; subnets → regional.
- Allocate ==nonoverlapping CIDRs== across cloud and enterprise.
- Reserve address capacity for endpoints, containers, and growth.
Routing & Connectivity
- Route tables → determine ==next-hop selection==.
- Peering → connectivity with platform-specific transit restrictions.
- Transit Gateway / Virtual WAN / NCC → connectivity hubs.
- Centralized inspection requires deliberate ==traffic steering==.
- Validate forward paths, return paths, and route propagation.
Hybrid & Multicloud
- Direct Connect / ExpressRoute / Cloud Interconnect → private connectivity.
- Site-to-site IPsec → encrypted connectivity over supported transports.
- BGP → exchange prefixes; apply ==route filtering==.
- Diverse circuits require independent facilities and failure domains.
- Validate ==MTU==, convergence, and asymmetric routing behavior.
Security & Segmentation
- Security groups / NSGs → distributed ==traffic filtering==.
- Network ACL behavior varies across cloud platforms.
- Cloud firewalls → centralized or distributed inspection.
- Private endpoints → private addressing for supported services.
- Apply ==least privilege== across workload and administrative paths.
DNS & Service Access
- Private DNS zones → internal ==name resolution==.
- Resolver endpoints → conditional forwarding across hybrid boundaries.
- Private endpoints require matching DNS resolution paths.
- Overlapping namespaces → ambiguous answers and troubleshooting complexity.
- Validate ==split-horizon DNS== from every consuming network.
Application Delivery & Egress
- L4 / L7 load balancers → distribute application traffic.
- Health probes → determine ==backend eligibility==.
- CDN / WAF → edge delivery and HTTP protection.
- NAT gateways / proxies → controlled outbound connectivity.
- Track ==SNAT capacity==, connection reuse, and idle timeouts.
Automation & Governance
- Terraform / OpenTofu → versioned ==network provisioning==.
- Reusable modules → approved connectivity and security patterns.
- Policy as code → enforce deployment constraints.
- Separate resource ownership, state, and deployment permissions.
- Detect ==drift==; review plans before applying changes.
Operations, Resilience & Cost
- Flow logs / metrics → establish ==traffic visibility==.
- Reachability analysis → evaluate supported configuration paths.
- Test zonal failures, circuit loss, and DNS outages.
- Measure throughput, latency, packet loss, and connection limits.
- Model ==data-transfer costs== across zones, regions, and egress.